// Compliance · System of Record
CLOUD2E CMMC Tracker
A self-contained, GCC High–ready compliance system of record that turns the day-to-day work of running a CMMC Level 2 / NIST SP 800-171 program into clean, exportable, assessor-ready evidence.
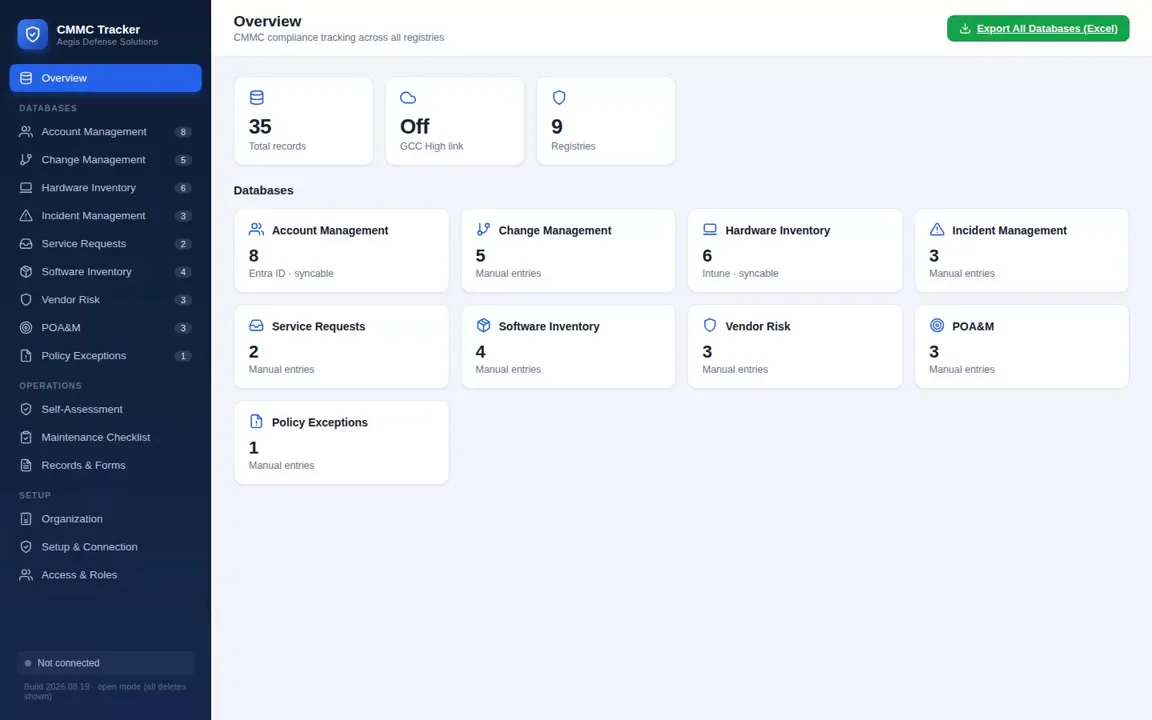
The CMMC Tracker is a single web application that consolidates every record a defense contractor needs to operate — and prove — a CMMC Level 2 program: the account, hardware, software, change, incident, vendor, and POA&M registries; a full 110-control NIST SP 800-171 self-assessment with live SPRS scoring; a recurring maintenance checklist with timestamped completion history; and a forms engine for the operational records in between.
It deploys as one Docker container inside your own Microsoft 365 GCC High tenant, stores everything in an embedded database under your control, and connects to Microsoft Entra ID and Intune with read-only, least-privilege permissions. Every registry and record exports to assessor-ready Excel, PDF, and ZIP evidence packages. In plain terms: CMMC certification tracking software that lives in your own tenant.
Included free for every CLOUD2E compliance client
// Who it's for
Built for the people who carry the program
DIB contractors
Defense Industrial Base companies pursuing or maintaining CMMC Level 2 certification.
MSPs & MSSPs
Providers running CMMC programs for multiple clients who need a repeatable, per-tenant system of record.
ISSMs, ISSOs & compliance leads
The people who have to produce evidence quickly for assessors, auditors, and primes.
GCC High enclaves handling CUI
Organizations operating in Microsoft 365 GCC High / Azure Government with Controlled Unclassified Information.
// Why teams choose it
The differentiators that survive a security review
Purpose-built for CMMC Level 2
Not a generic GRC tool bent into shape — every module maps to specific NIST SP 800-171 Rev. 2 practices and CMMC objectives, and the maintenance checklist follows the real daily-through-annual cadence of a Level 2 program.
GCC High–native, in your enclave
One container on Azure App Service inside your own Microsoft 365 GCC High environment. Graph calls use the sovereign endpoints, and CUI-adjacent compliance data never leaves your authorization boundary.
Read-only by design
The Tracker pulls identity and device facts from Entra ID and Intune with read-only, least-privilege Graph scopes. It cannot change a user, device, role, or policy — adopting it adds no new path to modify production.
One-click Graph connection
Setup is a single admin device-code sign-in. The app creates its own dedicated Entra app registration, encrypts its client secret, and grants itself only the read-only scopes it needs. No manual app registration.
Evidence by default
Every registry exports to Excel with live dropdown validations; every finalized form becomes a timestamped, CUI-bannered PDF; the whole system exports to a ZIP in one click. When an assessor asks "show me," the answer is one export away.
Immutable, defensible records
Records are editable as drafts, then finalized to lock them immutable. Finalizing an incident, risk assessment, or tabletop auto-creates POA&M entries — a connected, tamper-evident chain instead of scattered spreadsheets.
// Assessment & scoring
A live SPRS score you can defend
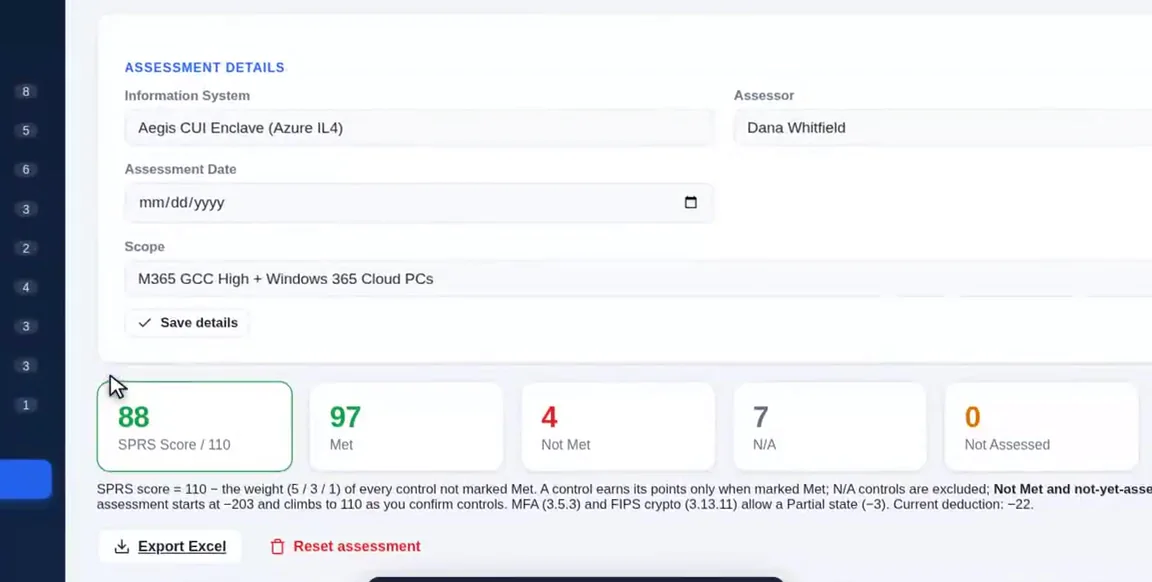
The self-assessment covers all 110 NIST SP 800-171 controls with per-control status, narrative, and notes — and computes your SPRS score with the DoD weighting model (5/3/1, including the defined partial-credit cases). Bulk-set helpers and full Excel import/export make a complete assessment fast to produce and painless to keep current.
Watch the number climb from −203 toward 110 as you confirm controls — and know exactly which practices are holding the score down.
// Inside the Tracker
Registries in. Evidence out.
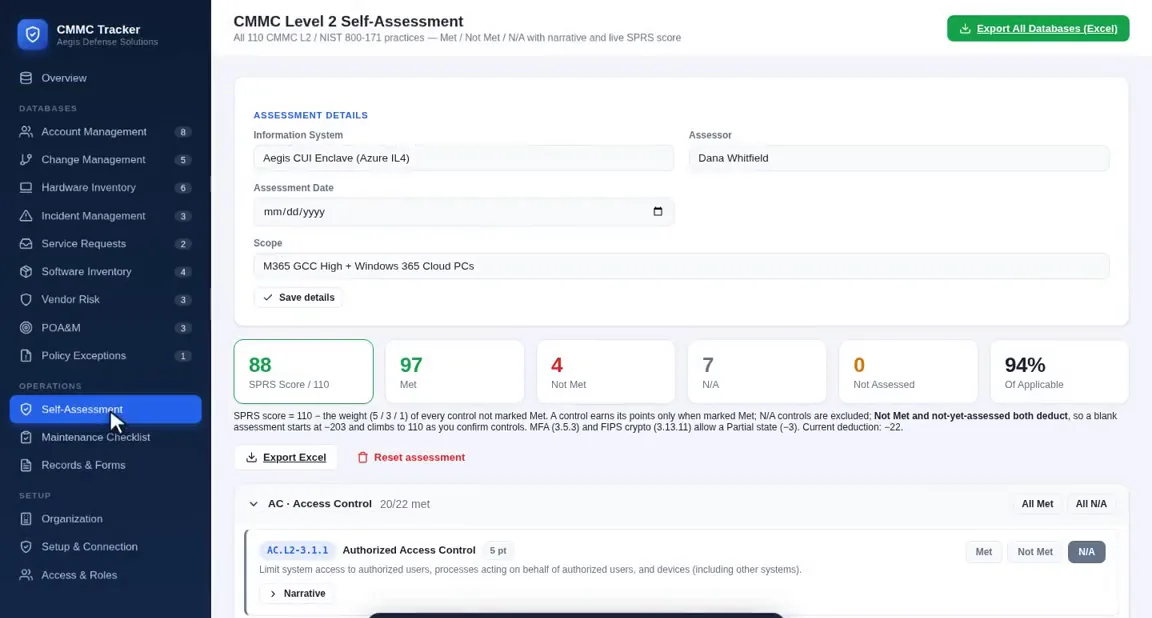
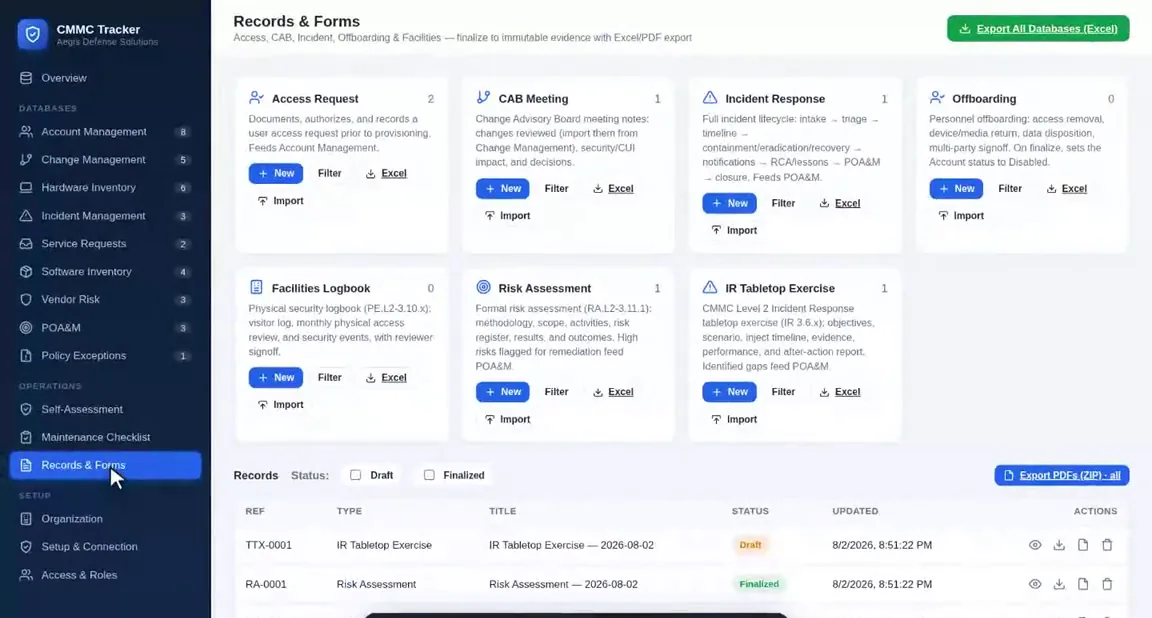
Screens from the Tracker demo environment (sample data). Prefer it moving? There's a 15-second tour in the Compliance section of the homepage.
// Capability areas
Nine areas. One system of record.
Asset & configuration registries
Hardware Inventory (device facts pulled read-only from Intune), Software Inventory with version control, and Change Management with security-impact analysis and rollback planning.
Identity & access records
The authoritative account register: identity synced read-only from Entra ID plus CUI authorization, privilege, training, and review history — paired with a signed user-agreements vault. Removed accounts are flagged, never silently deleted.
Assessment & scoring
A complete NIST SP 800-171 Rev. 2 self-assessment across all 110 controls with per-control narrative — and a live SPRS score computed with the DoD weighting model.
Continuous monitoring
A reusable cybersecurity maintenance checklist (daily through annual, plus event-driven) with timestamped run history, per-item results, evidence links, and reviewer sign-off.
Operational records & forms
Seven record types — Access Request, CAB Meeting, Incident Response, Offboarding, Facilities Logbook, Risk Assessment, and IR Tabletop — each with draft/finalize lifecycle and PDF/Excel export.
Risk & remediation
A standing vendor-risk register with foreign-influence classification, and a single POA&M where every finding lands — entered, imported, or auto-created on finalize.
Physical access kiosks
Two no-login kiosk pages — Ad-hoc Delivery and Entry Log — write finalized Facilities Logbook records from the front desk. A clipboard becomes structured PE-family evidence.
Evidence retention
A Post Assessment vault for final artifacts with a SHA-256 computed per file on upload — a tamper-evident drop zone for the deliverables that close out an assessment.
Governance & administration
Policy Exceptions, an Organization profile that pre-fills forms, self-provisioning setup with an environment health panel, and optional Entra sign-in with Approver and Technician roles.
// Built right
Small surface. Sovereign endpoints. Simple to audit.
The Tracker's architecture is deliberately boring — one container, one embedded database, no SaaS dependency — because the fewer moving parts a compliance tool has, the easier it is to trust, back up, and defend.
- Single-container architecture — an Express/Node.js server and React app; no sprawling microservice footprint to secure
- Embedded SQLite database under your control — back it up by copying a file, move it by moving a container
- Sovereign-cloud endpoints — all Microsoft calls go to GCC High / Azure Government (graph.microsoft.us, login.microsoftonline.us)
- Least-privilege, read-only integration — the tool can observe the tenant but never change it
- AES-256-GCM encryption at rest for the stored Graph client secret
- Manual, on-demand syncs — no background jobs reaching into the tenant; every sync is operator-initiated and auditable
- Build traceability — version, date, and build hash stamped on screen and into every export filename
- Deploys where your CUI already lives — behind the same Conditional Access and network controls as the rest of the enclave
Assessment-ready in minutes
The evidence an assessor asks for is already structured and one export away.
Lower risk to adopt
A read-only tool that cannot change production is an easy approval for security and leadership.
Stays in your boundary
Nothing about your compliance posture leaves your GCC High enclave.
No lock-in
Open Excel import/export on every module — your data is always portable.
Repeatable across clients
For MSPs: a clean per-tenant deployment pattern that standardizes every program.
One source of truth
Registries, assessment, monitoring, and records connected in one place.
Scope, stated plainly
The CMMC Tracker is the system of record and evidence layer over your CMMC program. The technical controls themselves are implemented by your Microsoft 365, Entra ID, Intune, Defender, and Sentinel stack — the Tracker documents, organizes, and evidences them. It does not detect incidents, enforce or change tenant settings, or transmit scores to SPRS on its own. That clear, bounded scope is exactly what makes it safe to deploy and trustworthy as an evidence source.
See the Tracker in your GCC High tenant
Tell us where you are today — we'll map the fastest, safest path and show you exactly what it takes.